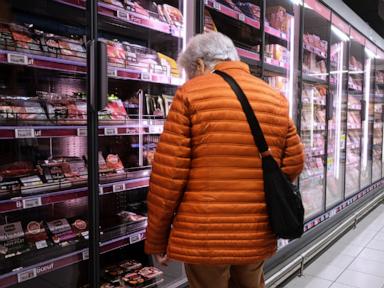
When hackers figured out how to remotely spike supermarket refrigeration temperatures across Europe, reaching up to 50°C and ruining millions of euros in stock, most people laughed it off as a bizarre sci-fi prank. They aren't laughing anymore. British food supply chains just got a sharp wake-up call as the fallout crossed the Channel, dragging UK meat processing and supply firms into an unexpected cyber crisis.
If you think a cyber-attack only means stolen credit cards or locked corporate laptops, you're missing the terrifying shift happening right now. Bad actors are moving past virtual screens and breaking into physical machinery. The recent cooling unit chaos proves that our everyday infrastructure is dangerously exposed.
The Reality Behind the Cold Chain Collapse
The incidents started rippling outward after European retail giants—including stores in Belgium, France, and Ireland—watched their commercial freezers mysteriously switch into defrost mode overnight. It wasn't magic. Attackers hunted down legacy refrigeration controllers connected directly to the internet using weak or default passwords.
By Monday morning, the shockwaves hit British shores. The Association of Independent Meat Suppliers (AIMS) confirmed that a handful of its roughly 300 members suffered direct collateral damage. Their refrigeration units heated up overnight, putting sensitive inventory at immediate risk.
While the UK's National Cyber Security Centre (NCSC) maintains that the national impact remains minimal and a spokesperson noted that agencies worked through the night to warn vulnerable operators, the underlying vulnerability is systemic. We've spent decades digitizing physical assets for efficiency without bothering to secure them against basic intrusion.
Why Legacy Technology Is a Ticking Time Bomb
For years, industrial facilities ran on isolated, closed-circuit systems. But modern logistics demand remote monitoring. Plant managers want to check freezer temperatures from their smartphones. Contractors want to update firmware from across the country.
To make this convenient, companies plugged old industrial control systems directly into the internet. They left default admin passwords untouched and skipped basic firewalls. Cybersecurity experts have warned about these gaps for years, but boardrooms treated IT security as an office expense rather than a physical survival metric.
Dr. Richard Horne, head of the NCSC, put it bluntly: society has gotten away with doing tech on the cheap for decades. End-of-life systems kept running long past their expiration dates, and necessary upgrades were routinely delayed to pad quarterly profit margins. Now, that penny-pinching is manifesting as spoiled inventory, disrupted food supplies, and targeted industrial sabotage.
The Absence of Ransom Demands Points to Sabotage
What makes these refrigeration hacks particularly unsettling is what's not happening. Unlike typical ransomware campaigns, the perpetrators aren't locking up servers and demanding millions in Bitcoin to hand over the decryption keys.
Security researchers tracking the attacks note a total lack of financial extortion. When hackers spend weeks probing industrial control systems only to crank up the heat until the food rots, it isn't about extortion. It's about disruption. It is a terrifying exercise in probing critical national infrastructure to see what breaks, how fast it breaks, and how the supply chain reacts.
For UK meat suppliers, who operate on razor-thin margins and strict temperature compliance laws, even a few hours of unexpected heat can mean writing off entire batches of high-value stock.
How Food Businesses Must Adapt Right Now
If you run a food processing plant, a cold storage facility, or a supply chain logistics firm, you cannot afford to wait for a government bulletin to check your security posture. The threat surface has expanded beyond office laptops.
Start with an aggressive asset inventory. Find every single connected thermostat, refrigeration controller, and automated valve in your facility. If a piece of equipment doesn't strictly need a direct connection to the external internet, disconnect it immediately.
If remote access is non-negotiable, isolate those systems behind heavily guarded Virtual Private Networks (VPNs), enforce multi-factor authentication, and change every single default factory password today. Audit your vendors and suppliers as well. Often, hackers don't break through your front door; they slip in through the third-party maintenance portal you forgot you gave access to.
The cooling units warming up across Europe and Britain aren't an isolated anomaly. They are a loud warning shot for the entire manufacturing sector. Secure your physical infrastructure before someone else does it for you.